

ShadowLock
ShadowLock detects and blocks unauthorized AI tools to prevent sensitive data leaks across your organization.
AI tool Details
Explore More
Alternatives
About ShadowLock
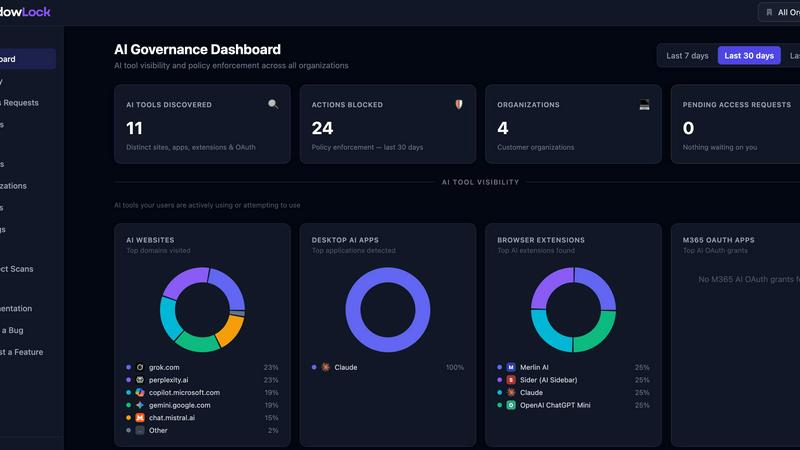
ShadowLock is a shadow AI detection and governance platform designed specifically for Managed Service Providers (MSPs) and internal IT teams. It provides real-time visibility and control over how employees use AI tools, before sensitive data leaves the endpoint. The platform addresses the blind spots that traditional managed-device controls miss: browser extensions, desktop AI applications, local Large Language Models like Ollama, and personal accounts used for AI access. ShadowLock deploys through a browser extension that intercepts and classifies risky pastes to AI sites, a Windows agent that blocks desktop AI apps and deploys silently via your existing RMM tool, and a multi-tenant dashboard that lets you audit or block each control with audit-ready reports. Built for MSPs to govern AI across every client from one central place, ShadowLock is private by design with no keystroke logging and zero content transmission to external servers. It covers over 100 AI tools, services, and desktop applications, giving organizations the ability to detect, classify, and block unauthorized AI usage that could expose customer records, credentials, intellectual property, and confidential documents to public AI platforms operating without enterprise agreements or data protection agreements.
Features
Endpoint Agent with RMM Integration
The ShadowLock Windows agent deploys silently to endpoints using your existing RMM tool, requiring zero user interaction and no dedicated security engineering. Once installed, it continuously monitors AI activity, scans for browser extensions, detects local AI applications like Ollama and LM Studio, and locks down AI features built into Chrome, Edge, Brave, and Firefox browsers. The agent provides persistent enforcement without disrupting user workflows, and all policy updates apply instantly across managed endpoints.
Browser Extension with Paste Interception
The browser enforcement layer self-configures automatically once the agent is installed on the endpoint. It intercepts pastes, file uploads, and sensitive data typed directly into AI prompts, classifying each interaction for risk. The extension enforces data-sharing opt-out settings on each AI tool automatically and applies your organization's policies with clear, user-facing messages that explain why certain actions are blocked or flagged. No user configuration is required.
Multi-Tenant Governance Dashboard
The centralized dashboard gives MSPs and IT teams a single pane of glass to manage AI governance across every client organization. From this dashboard, you can audit all detected AI activity, toggle controls on or off per client or per user group, and generate audit-ready compliance reports. The dashboard shows which AI tools are in use, which accounts are accessing them, and what types of data are being submitted, enabling informed policy decisions.
Privacy-First Architecture
ShadowLock is designed with privacy as a core principle. The platform performs no keystroke logging and transmits zero content from user interactions to external servers. All classification and policy enforcement happens locally on the endpoint, ensuring that sensitive data never leaves the device. This architecture supports compliance with HIPAA, GDPR, CCPA, and other privacy frameworks by eliminating data transmission risks while maintaining full visibility and control.
Use Cases
HIPAA Compliance for Healthcare Organizations
Healthcare organizations using ShadowLock can prevent patient data from being pasted into public AI chatbots like ChatGPT or Claude without a Business Associate Agreement in place. The platform detects ePHI being submitted to unapproved AI tools and blocks the action in real time, eliminating HIPAA exposure before a breach occurs. Audit reports provide documented evidence of compliance controls for regulatory reviews and incident response scenarios.
MSP Client Protection and Liability Reduction
MSPs deploy ShadowLock across all client endpoints from a single multi-tenant dashboard, establishing consistent AI governance policies enterprise-wide. When a client experiences an AI-related incident, the MSP has documented visibility and control measures in place, closing the gap between "not our job" and "you should have known." This reduces MSP liability and strengthens client relationships through proactive security management.
Intellectual Property Protection for Development Teams
Organizations with proprietary code and product plans use ShadowLock to prevent developers from submitting source code to AI coding assistants like GitHub Copilot and Cursor. The platform detects when proprietary code, credentials, or confidential documents are being entered into AI prompts and blocks the submission. This protects trade secrets and intellectual property from being absorbed into public AI training data.
Incident Response Readiness
ShadowLock provides complete visibility into which AI tools were used, which accounts accessed them, and what types of data were involved in any AI-related incident. Without this prior visibility, organizations cannot answer these critical questions, breaking triage, notification obligations, and defensibility. ShadowLock's audit trails enable rapid, documented incident response that supports legal and regulatory requirements.
Frequently Asked Questions
How does ShadowLock deploy across client environments?
ShadowLock deploys silently via your existing RMM tool. The Windows agent installs without user interaction, and the browser extension self-configures once the agent is detected on the endpoint. IT teams configure policies once in the multi-tenant dashboard, and those policies apply automatically to all managed endpoints without per-device configuration or dedicated security engineering resources.
Does ShadowLock capture or transmit user content?
No. ShadowLock performs no keystroke logging and transmits zero content from user interactions to external servers. All classification, policy enforcement, and data analysis happens locally on the endpoint. The platform only sends metadata about which AI tools were accessed and whether actions were blocked or allowed, preserving user privacy while maintaining full visibility and control.
What AI tools and applications does ShadowLock detect and govern?
ShadowLock currently detects and governs over 100 AI tools, services, and desktop applications, including public chatbots like ChatGPT, Claude, and Gemini, AI browser extensions, embedded SaaS AI features like Copilot, desktop AI apps including Claude Desktop and Ollama, AI coding assistants like GitHub Copilot and Cursor, and meeting transcription AI tools like Otter.ai and Fireflies. The platform continuously updates its detection capabilities.
Can ShadowLock block AI usage on personal accounts?
Yes. ShadowLock detects when employees use personal accounts to access AI tools on managed devices, which is a common blind spot for organizations. Since personal accounts operate under consumer terms with no DPA, BAA, or incident notice obligations, this creates significant legal exposure. ShadowLock intercepts data submissions regardless of the account used and enforces your organization's policies consistently.
Similar to ShadowLock
SnitchFeed
SnitchFeed is an agentic social listening tool that surfaces high-intent conversations on LinkedIn, X, Hackernews, and more for GTM and product teams.
RunwayAI
Independent Runway AI video generator for text and image-to-video workflows, with task tracking, previews, downloads, and API access.
Happy Horse AI
Create videos from text, images, or references with Happy Horse AI using flexible 720P/1080P output and API workflows.
Labrynth AI
AI regulatory intelligence platform that turns complex requirements into cited, audit-ready outputs.
StackLedge
A strictly vetted discovery engine exclusively for APIs, developer tools, and advanced AI agents. We manually block all low-effort SaaS wrappers.
Text Logo
Create a custom text logo, wordmark logo, or typography logo with editable fonts, colors, icons, shapes, and flexible export formats.
Built2WinWeb
MCP, A2A, and llms.txt generation. Custom PHP websites built for AI agent discovery and indexing — flat‑fee, full ownership, no monthly fees.